Free checklist
CIP-003-9 Section 6 readiness checklist
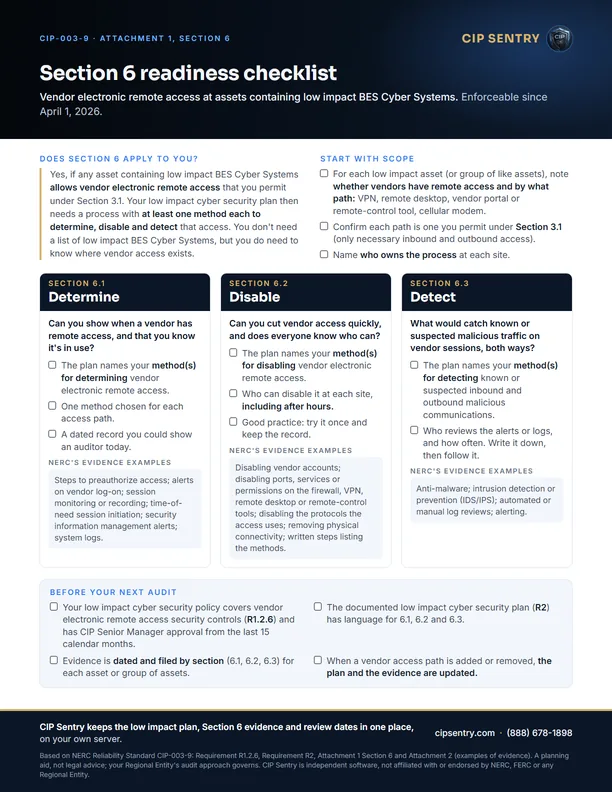
Since April 1, 2026, low impact assets that allow vendor electronic remote access need a way to determine, disable and detect it. This one-page checklist helps you check both the plan and the evidence.
What’s on the page
- Whether Section 6 applies to you, and how to scope each vendor access path
- Plan language and practical checks for 6.1 Determine, 6.2 Disable and 6.3 Detect
- The evidence examples NERC lists in Attachment 2
- A before-your-audit list, including the R1.2.6 policy approval
No sign-up, no email required. Prepared by CIP Sentry. A planning aid, not legal advice; your Regional Entity’s audit approach governs.
The three questions behind Section 6
Section 6.1
Determine
Can you show when a vendor has remote access, and that you know it’s in use?
Section 6.2
Disable
Can you cut vendor access quickly, and does everyone know who can?
Section 6.3
Detect
What would catch known or suspected malicious traffic on vendor sessions, in both directions?
For the background, read CIP-003-9 vendor remote access: a practical guide, or see how CIP Sentry runs a low impact program.
Request a quote
See CIP Sentry on your own terms.
Get a quote sized to your registered functions and impact levels, and a live walkthrough on sample data. No sales pressure, no cloud account, no commitment.